
 Download

A project devoted to secure programming in the Go language. Licensed under the Apache License, Version 2.0 (the "License"). You may not use this file except in compliance with the License. You can integrate third-party code analysis tools with GitHub code scanning by uploading data as SARIF files. The workflow shows an example of running the gosec as a step in a GitHub action workflow that outputs the results.sarif file. The workflow then uploads the results.sarif file to GitHub using the upload-serif action. Gosec can be configured to only run a subset of rules, to exclude certain file paths, and produce reports in different formats. By default, all rules will be run against the supplied input files.
Features
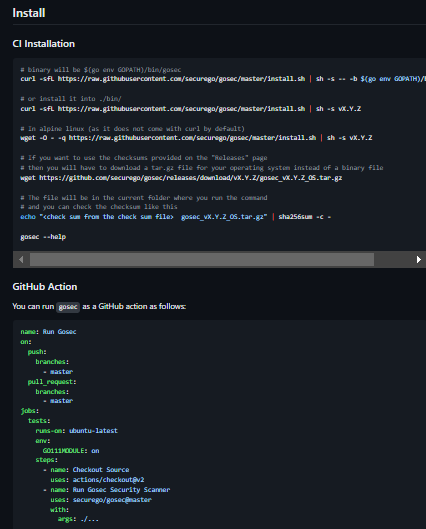
- CI Installation
- You can run gosec as a GitHub action
- Integrate with code scanning
- Gosec can be configured to only run a subset of rules
- Exclude certain file paths
- Produce reports in different formats
Project Samples
Categories
Static Code AnalysisLicense
Apache License V2.0Follow gosec
Other Useful Business Software
Build Securely on AWS with Proven Frameworks
Moving to the cloud brings new challenges. How can you manage a larger attack surface while ensuring great network performance? Turn to Fortinet’s Tested Reference Architectures, blueprints for designing and securing cloud environments built by cybersecurity experts. Learn more and explore use cases in this white paper.
Rate This Project
Login To Rate This Project
User Reviews
Be the first to post a review of gosec!
