
 Browse Code

The project covers the digital forensics investigation of the Windows volatile memory.
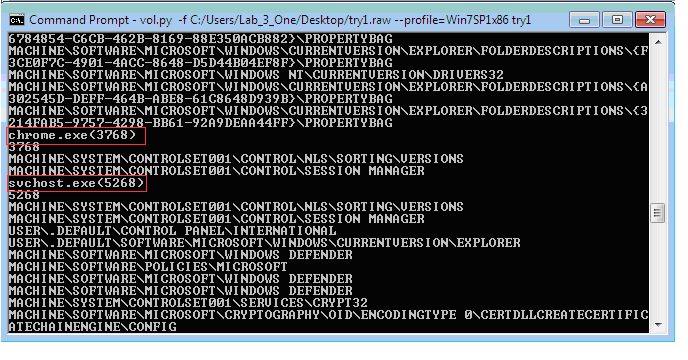
A plug-in for the volatility tool is implemented to extract the Windows 7 registry related information such as registry key value, name specific to the user activity from the volatile memory dump. The plug-in also provides the information about registry keys accessed by the running process from the Windows volatile memory dump.
Features
- The project covers the digital forensic investigation of Windows volatile memory
- A plug-in for the volatility tool to extract specific Windows registry key values related to the user activity from the volatile memory dump is proposed..
Project Samples


Follow Digital Forensics
Other Useful Business Software
Save Up to 91% on Cloud Compute With Spot VMs
Run batch jobs at 60-91% off with Spot VMs. Long-running workloads get automatic discounts with sustained use.
Rate This Project
Login To Rate This Project
User Reviews
Be the first to post a review of Digital Forensics!